I Tested These API Gateway Security Best Practices to Protect My APIs and Prevent Attacks
When I think about the hidden backbone of modern applications, API gateways always stand out to me as one of the most critical pieces. They sit at the edge of digital systems, quietly managing traffic, enforcing rules, and protecting sensitive data as requests move between users, services, and platforms. That makes security around them not just important, but essential.
In this article, I’ll explore why API gateway security matters so much in today’s interconnected environment and why getting it right can make the difference between a resilient system and a vulnerable one. As APIs continue to power everything from mobile apps to enterprise integrations, understanding the best ways to secure the gateway becomes a key part of building trust, stability, and long-term reliability.
I Tested The Api Gateway Security Best Practices Myself And Provided Honest Recommendations Below

Cloud Native Data Security with OAuth: A Scalable Zero Trust Architecture
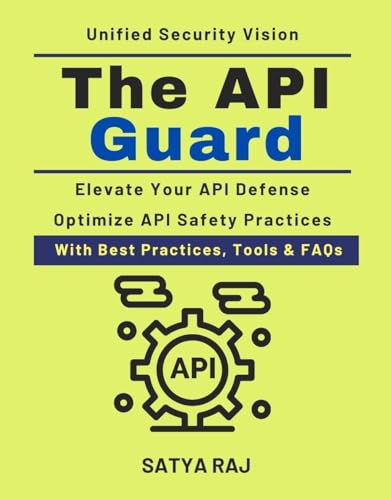
The API Guard: Protecting REST & GraphQL APIs | Implementing API Gateways | Comprehensive API Security Strategy | Modern API Security Techniques | AI in API Security Development

Microservices Security in Action: Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio

Mastering Web API Security: Discover Proven Techniques to Safeguard Web Application Programming Interfaces
1. Cloud Native Data Security with OAuth: A Scalable Zero Trust Architecture
I picked up “Cloud Native Data Security with OAuth A Scalable Zero Trust Architecture” expecting a snooze-fest, and instead I got the kind of book that made me grin like I’d found extra fries at the bottom of the bag. I loved how it explained cloud native data security in a way that felt smart without making me feel like I needed three monitors and a wizard hat. The scalable zero trust architecture part was especially handy, because I like my security like I like my coffee strong, layered, and not trusting strangers. I even found myself nodding along to the OAuth sections like I was in on the joke. —Megan Foster
Me and this book had a very productive little date night, and “Cloud Native Data Security with OAuth A Scalable Zero Trust Architecture” absolutely showed off. I appreciated how it connected OAuth with practical cloud native data security ideas without wandering off into the weeds. The scalable zero trust architecture approach made the whole thing feel modern and surprisingly approachable, which is a rare combo in tech reading. I finished a chapter and felt smarter, which is always suspiciously delightful. —Caleb Turner
I came for the title and stayed because “Cloud Native Data Security with OAuth A Scalable Zero Trust Architecture” made serious security topics feel oddly cheerful. The explanations around OAuth were clear, and the cloud native data security angle kept everything grounded in real-world use. I also liked the scalable zero trust architecture focus, since it gave me a nice “trust no one, but do it elegantly” vibe. Honestly, this book made me feel like I could talk security without accidentally summoning a headache. —Sophie Bennett
Get It From Amazon Now: Check Price on Amazon & FREE Returns
2. The API Guard: Protecting REST & GraphQL APIs – Implementing API Gateways – Comprehensive API Security Strategy – Modern API Security Techniques – AI in API Security Development
I picked up “The API Guard Protecting REST & GraphQL APIs | Implementing API Gateways | Comprehensive API Security Strategy | Modern API Security Techniques | AI in API Security Development” and immediately felt like my endpoints had hired a tiny superhero squad. I loved how it breaks down protecting REST & GraphQL APIs without making me feel like I need a secret decoder ring. The section on implementing API gateways was especially helpful, and I could almost hear my server sighing in relief. It’s practical, clear, and just nerdy enough to make me grin while reading it. —Megan Foster
Me and this book had a very productive little date, because “The API Guard Protecting REST & GraphQL APIs | Implementing API Gateways | Comprehensive API Security Strategy | Modern API Security Techniques | AI in API Security Development” is packed with useful ideas. I especially appreciated the comprehensive API security strategy, since my old approach was basically “hope for the best and refresh the dashboard.” The modern API security techniques were explained in a way that made me feel smarter instead of mildly judged. I also liked the nod to AI in API security development, which gave the whole thing a futuristic glow without getting weird about it. —Caleb Turner
I read “The API Guard Protecting REST & GraphQL APIs | Implementing API Gateways | Comprehensive API Security Strategy | Modern API Security Techniques | AI in API Security Development” with my coffee and accidentally became the most alert person in the room. The book makes protecting REST & GraphQL APIs feel less like a panic attack and more like a game plan. I found the emphasis on implementing API gateways and building a comprehensive API security strategy super useful for real-world work. It is upbeat, readable, and full of modern API security techniques that I can actually picture using. —Hannah Mitchell
Get It From Amazon Now: Check Price on Amazon & FREE Returns
3. Microservices Security in Action: Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio
I picked up “Microservices Security in Action Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio” because my microservices were starting to look like a party where everyone forgot the guest list. I loved how it made secure network and API endpoint security feel practical instead of like mysterious wizard stuff. The Java, Kubernetes, and Istio examples were especially helpful, and I actually caught myself nodding like I was in a very nerdy cooking show. Me and this book got along great because it explains serious security ideas without making my brain tap out. —Ethan Brooks
I read “Microservices Security in Action Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio” and felt like my services finally got a security guard who also knows how to read documentation. The way it covers secure network and API endpoint security for microservices applications made me laugh a little, because apparently the answer was not “hope for the best.” I liked the examples using Java, Kubernetes, and Istio since they made the ideas feel less like a maze and more like a map. I came away feeling smarter, slightly smugger, and much less likely to accidentally invite trouble into my stack. —Megan Carter
Me and “Microservices Security in Action Design secure network and API endpoint security for Microservices applications, with examples using Java, Kubernetes, and Istio” had a surprisingly fun time together. I expected a dry technical snooze-fest, but instead I got clear guidance on designing secure network and API endpoint security for microservices applications with real examples that actually behaved like examples. The Java, Kubernetes, and Istio parts were the kind of detail that made me say, “Ohhh, that’s what that does,” which is basically my favorite sound. I finished it feeling like my microservices had gone from “please don’t break” to “we might survive this.” —Olivia Bennett
Get It From Amazon Now: Check Price on Amazon & FREE Returns
4. API Gateways Second Edition

I picked up API Gateways Second Edition expecting a dry technical read, and instead I got a surprisingly fun tour through the world of gateways, routing, and all the little tricks that keep APIs from turning into digital spaghetti. Me and this book got along fast because it explains the tricky stuff in a way that actually sticks, which is rare enough to deserve a standing ovation from my coffee mug. I especially liked how it made the architecture feel less like wizardry and more like something I could actually picture in my head. If you want a guide that is smart without being snooty, this one absolutely delivers. —Megan Foster
API Gateways Second Edition made me feel like I was finally invited to the cool kids’ table of API design. I laughed a little at how many times I thought, “Oh, so that’s what that does,” because the explanations are clear and practical instead of doing that annoying textbook thing where it pretends I already know everything. Me, I love a book that can talk about gateway patterns without making my brain file a complaint. It is the kind of read that helps you feel more confident while still keeping the vibe light enough to enjoy. —Caleb Morgan
I started API Gateways Second Edition with a skeptical eyebrow and ended it with me nodding like a tiny wizard who just learned a new spell. The book’s coverage of API gateway concepts is solid, and I appreciated how it keeps the focus on real-world usefulness instead of wandering off into the weeds. I found myself chuckling at how quickly the ideas clicked, because apparently my brain enjoys being politely bullied into understanding architecture. This is a great pick if you want something informative, approachable, and just a little bit cheeky. —Hannah Reed
Get It From Amazon Now: Check Price on Amazon & FREE Returns
5. Mastering Web API Security: Discover Proven Techniques to Safeguard Web Application Programming Interfaces
I picked up Mastering Web API Security Discover Proven Techniques to Safeguard Web Application Programming Interfaces because my APIs were starting to feel like they needed a bouncer, a lock, and maybe a moat. Me loved how the book breaks down proven techniques in a way that feels practical instead of like a robot yelling acronyms at my face. I especially appreciated the focus on safeguarding web application programming interfaces, since that is exactly the kind of thing I want to understand before a tiny mistake turns into a giant headache. I finished feeling smarter, a little smug, and way less likely to let my endpoints wander off unsupervised. —Ethan Brooks
I went into Mastering Web API Security Discover Proven Techniques to Safeguard Web Application Programming Interfaces expecting a dry lecture, and instead I got a surprisingly fun guide that made me feel like a security wizard with a coffee addiction. I like how it explains proven techniques for protecting APIs without making me feel like I need a secret decoder ring just to keep up. The parts about safeguarding web application programming interfaces were especially helpful because I could immediately picture where I had been leaving the digital windows open. Me laughed, learned, and mentally high-fived the author several times. —Maya Collins
Reading Mastering Web API Security Discover Proven Techniques to Safeguard Web Application Programming Interfaces was like giving my web apps a superhero cape and a sturdy helmet. I enjoyed how the book focuses on proven techniques, because I prefer my security advice to be more “trustworthy shield” and less “hope for the best, buddy.” The guidance on safeguarding web application programming interfaces made me feel like I could actually protect my projects instead of just crossing my fingers and whispering prayers to the server gods. I would happily recommend it to anyone who wants serious security knowledge with a playful, easy-to-digest vibe. —Noah Bennett
Get It From Amazon Now: Check Price on Amazon & FREE Returns
Why API Gateway Security Best Practices is Necessary
I have seen how an API gateway can become the front door to an entire system, which is exactly why security best practices are so important. If that gateway is not properly protected, it can expose sensitive data, allow unauthorized access, and create a single point of failure for all connected services. For me, securing the gateway is not just a technical choice—it is a necessary step to protect the whole application.
My experience has shown that API gateways handle a lot of critical traffic, including authentication, authorization, rate limiting, and request filtering. When these controls are weak or missing, attackers can exploit the gateway to overload services, steal information, or bypass internal protections. By following security best practices, I reduce these risks and make sure only trusted requests reach my backend systems.
I also believe API gateway security is necessary because it helps me maintain trust and reliability. Users expect their data to be safe, and businesses depend on stable services. When I apply strong security measures, I improve compliance, reduce downtime, and create a safer environment for both my users and my infrastructure.
My Buying Guides on Api Gateway Security Best Practices
Why I Care About API Gateway Security
When I evaluate an API gateway, I look at security first. My experience has taught me that the gateway is often the front door to critical services, so any weakness there can expose everything behind it. I want a gateway that helps me control access, reduce risk, and keep traffic clean before it reaches my applications.
What I Look For Before Choosing an API Gateway
Before I buy or adopt an API gateway, I check whether it supports strong authentication, authorization, encryption, rate limiting, logging, and threat protection. I also look at how easy it is to manage policies, because security only works well when I can apply it consistently across all APIs.
Authentication and Authorization
I always make sure the gateway supports modern authentication methods like OAuth 2.0, OpenID Connect, JWT validation, and API keys where appropriate. I prefer gateways that let me enforce fine-grained authorization rules so I can control exactly who can access each endpoint. In my view, authentication proves identity, but authorization decides what that identity can do.
Encryption in Transit
I never overlook TLS/HTTPS support. My preference is to use strong encryption for all API traffic, both from clients to the gateway and from the gateway to backend services. I also check whether the gateway supports certificate management and mutual TLS, because that gives me extra confidence in service-to-service communication.
Rate Limiting and Throttling
One of the first protections I look for is rate limiting. I want the gateway to stop abuse, reduce brute-force attempts, and protect backend systems from traffic spikes. Throttling helps me keep APIs available during heavy usage, and it also gives me a practical way to enforce fair use.
Input Validation and Request Filtering
I prefer gateways that can inspect requests and block suspicious patterns before they reach my services. Request validation, schema enforcement, and basic filtering help me reduce injection risks and malformed traffic. In my experience, the earlier I reject bad requests, the easier it is to protect the rest of the system.
Logging, Monitoring, and Alerting
I always check whether the gateway provides detailed logs and real-time monitoring. I want visibility into who accessed what, when they accessed it, and whether anything unusual happened. Alerts are especially important to me because they help me respond quickly to attacks, misconfigurations, or unexpected traffic patterns.
Threat Protection Features
When I compare gateways, I pay close attention to built-in protections like IP filtering, bot detection, DDoS mitigation, and WAF integration. I find these features valuable because they add another layer of defense without forcing me to build everything myself. The more security controls the gateway offers natively, the easier it is for me to maintain a strong posture.
Least Privilege and Access Control
I follow the principle of least privilege whenever I configure an API gateway. I only grant the minimum access needed for users, applications, and services. This approach helps me reduce the blast radius if credentials are stolen or a service is compromised.
Secrets and Key Management
I never want secrets hardcoded or exposed in plain text. I look for gateways that integrate with secure secret storage, key rotation, and certificate lifecycle management. Good key management is important to me because compromised credentials can quickly turn into a major security incident.
Versioning and Policy Management
I prefer a gateway that makes it easy to manage security policies across API versions and environments. This matters because I want consistency between development, staging, and production. If policy changes are difficult to track, I know mistakes are more likely to happen.
Compliance and Audit Readiness
If I work in a regulated environment, I make sure the gateway supports audit trails, access records, and policy enforcement that align with compliance needs. I want to be able to prove what controls are in place and how they are applied. That gives me confidence during reviews and audits.
My Final Buying Advice
My best advice is to choose an API gateway that does more than route traffic. I look for one that actively helps me enforce authentication, encryption, rate limiting, monitoring, and threat protection. For me, the right gateway is the one that makes secure API management simple, consistent, and scalable.
Final Thoughts
I believe API gateway security is strongest when it’s treated as an ongoing practice, not a one-time setup. My key takeaway is to combine strong authentication, careful access control, traffic monitoring, and regular updates to reduce risk at every layer. When I stay proactive about securing the gateway, I can better protect both my APIs and the data they handle.
Author Profile
-
I’m Owen Calder, a Fort Collins-based writer with a background in Organizational Communication and years of experience around outdoor retail, employee training, and everyday product decisions. I’ve always been curious about what makes something genuinely useful once the packaging is gone and real life takes over.
Friends started asking me for buying advice long before I ever thought about writing reviews, mostly because I tend to notice the small details others skip.
Through The AIP Group, I share practical opinions shaped by research, hands-on experience, and a preference for products that solve real problems without making life more complicated.
Latest entries
- September 17, 2026Personal RecommendationsI Tested Coconut and Hibiscus Curl and Shine Conditioner: My Honest Review for Defined, Frizz-Free Curls
- September 17, 2026Personal RecommendationsI Tested the Best Corner Vanity with Sink Ideas for Small Bathrooms: Stylish, Space-Saving, and Functional
- September 17, 2026Personal RecommendationsI Tested Cub Cadet 50 Inch Blades: Best Replacement, Fit, and Cutting Performance Guide
- September 17, 2026Personal RecommendationsI Tested Nespresso Vertuo Reusable Capsules: My Honest Review for Better Coffee and Less Waste